

The five identities
The request ID, Session ID and Cookie ID describe one identification, one browsing session and the browser’s storage. They group and join identifications; the Identifiers page covers how each one is built and how long it lasts.
How identities link
Each identification carries exactly one visitor, one device and one public IP, and at most one user and one local IP. An anonymous identification has no user. Identities that share an identification are linked, and the links build up over time:- A user links to the devices, visitors, public IPs and local IPs its identifications came from, and to the countries behind them.
- A device links to the accounts signed in on it, the visitors its cookies created and the IP addresses it used.
- A visitor links to its device and to the accounts and IP addresses seen with it.
- A public IP links to the accounts, devices and visitors seen behind it, and to the local IPs they reported.
The risk of a user, device, visitor or IP
Only an identification has a number: its Risk Score, from 0 to 100. A user, device, visitor or IP address carries a band word instead, the worst band among its identifications in the period you look at: Trusted (0 to 29), Suspicious (30 to 59) or Dangerous (60 to 100). A user with twenty Trusted identifications and one Dangerous identification is Dangerous, so one masked or automated signup is enough to mark the account. The webhook and the History API carry the Risk Score of each identification, and your backend maps it to a band. For an identity’s band, read its identifications and take the highest Risk Score, skipping any value above 100 (the999 rate-limit marker). Risk Scoring covers the bands in full.
High-Risk Events belong to users
ShieldLabs detects four High-Risk Events directly on your users, out of the box, without building rules or training a fraud model:- Multi-accounting: several accounts run by one person, linked through the devices and network they share. By default it fires from 3 accounts on one visitor, and the threshold is configurable.
- Account sharing: one account used from several distinct devices. By default it fires from 4 devices on one account, and the threshold is configurable.
- Impossible travel: an account appearing in locations it could not reach in the time between them.
- Account takeover: an existing account appearing in a new environment that points to someone else using it.
The User HID is your account key
Pass a hashed User HID withcheckAuthenticatedUser on every signed-in page. Users, account-level risk and all four High-Risk Events are built on it.
Use a hashed or pseudonymous value, never a raw email or login, and apply the same transform every time so one account always maps to one User HID:
checkAnonymous(). The webhook then carries "user_hid": "anonymous", and the identification still links to its device, visitor and IP addresses. The snippet setup covers both calls.
Read an identity in code
The History API returns every identification of one identity when you search by its key:user_hid, device_id, visitor_id or ip. To read what one account did:
{ "data": [...], "total": N }, one row per identification. Page with offset when an account has more than 100 identifications. From the rows, skip any score above 100 (the 999 rate-limit marker), take the highest remaining score for the account’s band, and collect the distinct device_id (ignoring the all-zero Device ID), visitor_id and ip values for its linked devices, visitors and public IPs. Each Private API Key reads one domain, so read each domain with its own key. Reads are free.
Read every identification of one account has the full recipe.
In the analytics dashboard
Users, devices, visitors and public IPs each have a card in the analytics dashboard with a risk band and linked identities; local IPs appear on those cards as linked local IPs, with the identifications behind each. The band on a card is the worst band of the identity’s identifications in the selected period, and a user’s card also shows its High-Risk Events with their confidence. Find your identities on the Users, Devices, Unique visitors and Public IPs tabs of Analytics, and open any identifier to reach its card. User, device, visitor and IP cards covers each part of a card.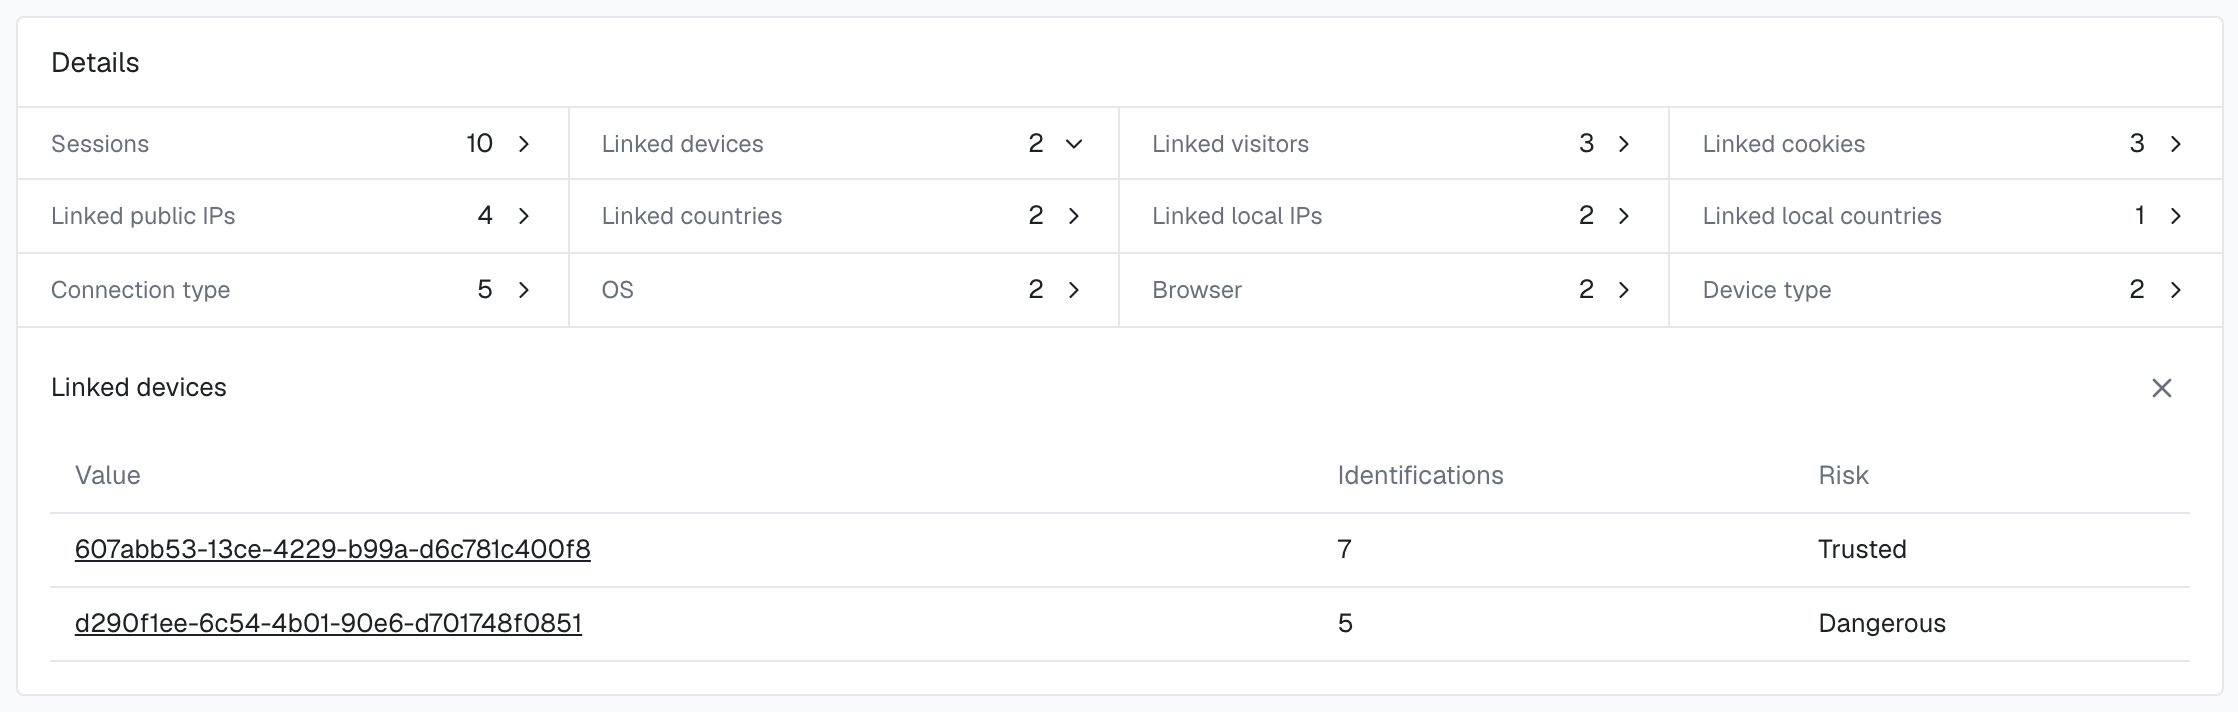
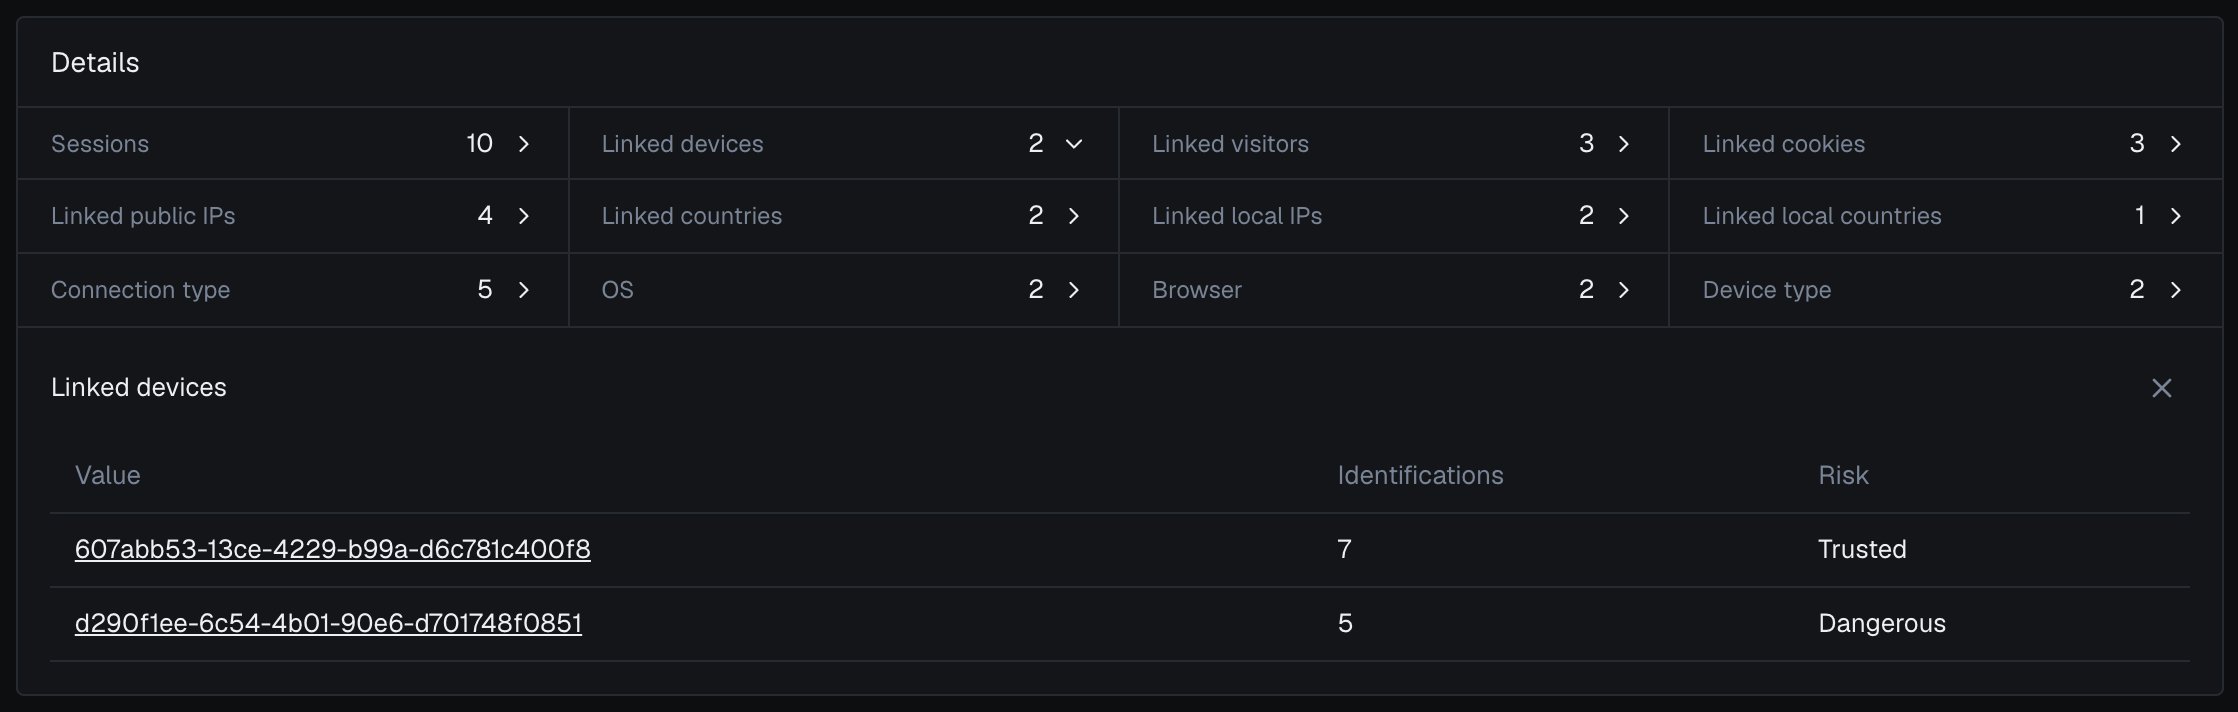
The devices linked to one user in the analytics dashboard, with the band of the identifications they share.
Next steps
Accounts and identifications
How the account behind many identifications and the identification in front of you work together.
Identifiers
How each identifier is built, how long it lasts and what the webhook carries.
High-Risk Events
Multi-accounting, account sharing, impossible travel and account takeover, detected on your users.
Risk Scoring
The 0 to 100 Risk Score of each identification and the band of every user, device, visitor and IP.